[ November 17, 2026 ]
Yes, something is going on. Some line has been crossed in what hackers and foreign adversaries can do. Whether any of these incidents amounts to terrorism is a separate question. But the advance in hacking weaponry is real. AI is giving attackers the ability to strike faster and at a scale that once took far more people, time and resources.
The power of AI can not be underestimated. And so we must defend with AI – AI against AI.
AI has been deployed in the hackers’ toolbox. A major threshold has been crossed, driven by the shift from simple AI chatbots to autonomous AI agents that can plan and execute complex attacks at machine speed. Wide scale attacks are now no brainer. It seems rather sudden that these highly effective wide scale attacks (Europe, now here) have all suddenly begun to role out in the past couple of weeks. The hackers were always hacking the time – ransomware, malware, etc etc but this is a whole other level.
ADVERTISEMENT
Google and Mandiant reported Monday that they’ve observed attackers using AI agents to carry out multiple stages of an intrusion at machine speed. That’s a real change. If attackers can automate work that used to require skilled people at each step, they can go after more targets in less time. It makes attacks cheaper to attempt and faster to repeat.
According to a Google Threat Intelligence Group report, attackers have reached a “critical inflection point” by deploying multi-agent frameworks (such as Artex, Cairn, and PentAGI) that automatically chain together reconnaissance, vulnerability scanning, and network lateral movement without human step-by-step commands.
- Attacks at Machine Speed. Security researchers at TechRadar and Pace University note that AI has compressed the timeline between finding a flaw and launching an intrusion from days down to minutes. Traditional defense teams built to respond at human speed are struggling to keep up. [1, 2]
- Lowering the Barrier for Amateurs. Complex breaches no longer require elite state-sponsored teams. For example, CrowdStrike investigators recently traced a massive wave of breaches across nine major South Korean banks to a single 26-year-old amateur who leaned heavily on AI tools to execute the attacks
The European cases are the strongest part of your argument. In early November, hackers tampered with supermarket refrigeration across eight countries around the same time that three French regional blood banks were hit. Staff moved the blood to disconnected refrigerators, preserving the supply. A similar attack hit hundreds of French supermarkets in October, and France attributed that earlier attack to Iran’s Revolutionary Guard. Public reporting hasn’t established that AI was used in either episode. reuters.com
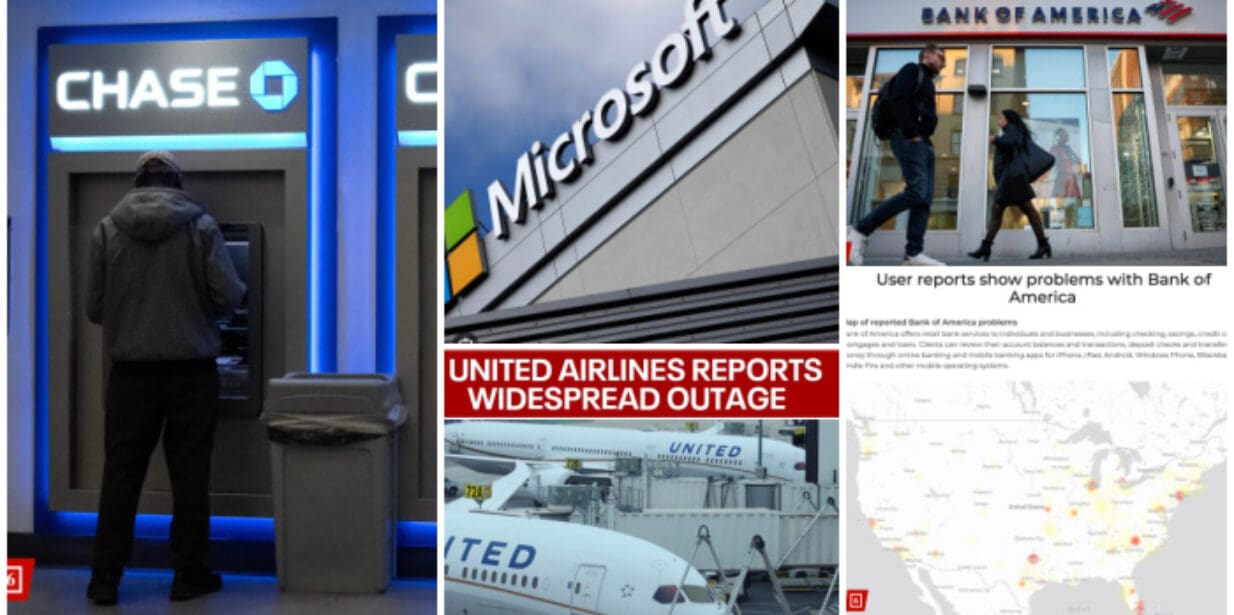
The U.S. cases are less clear. Chase blamed a software bug. The FAA said a flood of connection attempts destabilized legacy equipment, and federal officials said they saw no indication of a cyberattack. The FAA’s account explains what overwhelmed the system. It doesn’t establish who or what generated the traffic. www.axios.com
My read is that the shift is in how much damage a small team could do in a short time. The timing of these incidents makes the question worth asking. Google’s findings give us a concrete reason to take it seriously even if the U.S. outages and the European attacks turn out to have entirely separate causes.
ADVERTISEMENT
Workday, a business software that handles payroll and human resources management for thousands of prominent companies, suffered a major outage Friday, joining Microsoft in experiencing a shutdown this week.
The platform manages services for 11,500 companies.
Why Chase, Microsoft and United are facing crippling outages — and why it’s all likely to get worse
By Jared Downing, NY Post, November 17, 2026:
If it feels like the entire internet is in limbo right now — with major outages from Microsoft, JPMorgan Chase bank and United Airlines in the span of a few days — that’s because it is, cyber security experts say.
And it’s probably going to get worse before it gets better.
Major companies that underpin the entire digital economy are in a mad rush to update their complicated and often outdated computer systems as AI tools come online.
ADVERTISEMENTThere’s also a deadline to get this done before the holiday rush, when spending swells and more back-office employees take time off.
“It’s holiday time, it’s travel time, it’s shopping. So you have all those higher spikes in volume, and more pressure to [update your systems,]” Marva Bailer, CEO of tech advisory firm Qualaix, told The Post.
Legacy systems are looking increasingly like Frankenstein’s monster, with bolted-on parts from AI companies and third-party vendors offering more points of failure, she said.
That appears to be exactly what happened with Monday’s outage at Chase. The bank said a software bug within its systems caused a failure — but it also impacted related transactions with Zelle, Bank of America, Capital One, Wells Fargo, according to multiple reports.
Also on Monday, United Airlines was forced to halt all departing flights thanks to a technical problem with its system.
Continued…….
There are steps we can take. According to Gemini:
To counter AI-speed attacks, security experts agree that defenses must also move to machine speed, pairing autonomous AI security tools with stricter basic protections for older infrastructure. Because attackers now automate the hunt for weak spots, relying on slow, manual human responses is no longer enough.
1. Immediate Actions for Individuals
While large networks and industrial systems are the primary targets of this recent wave, individual accounts are frequently used as stepping stones into larger systems.
- Switch to Phishing-Resistant Authentication. Replace SMS text codes with hardware security keys or passkeys. AI can easily craft convincing fake login pages, but passkeys and physical keys will not work on fraudulent websites.
- Enable Automatic Updates Everywhere. Because AI agents scan for newly announced software flaws within minutes, turn on automatic updates for your phone, computer, web browsers, and home Wi-Fi router.
- Lock Down Smart Home Devices. Place internet-connected cameras, thermostats, and appliances on a separate guest Wi-Fi network so a compromised gadget cannot give an attacker access to your main computer or phone.
- Use Unique Passwords and Freeze Your Credit. Use a password manager so one breached site cannot compromise your email or banking. Keep your credit frozen at all three major bureaus (Equifax, Experian, and TransUnion) to block automated identity theft.
2. Critical Shifts for Businesses and Organizations
Security leaders and government agencies recommend several urgent changes to stop autonomous attacks before they spread:
- Deploy “AI vs. AI” Autonomous Defense. Security teams cannot out-type an AI agent. Organizations are increasingly deploying defensive AI agents capable of automatically isolating infected computers, blocking suspicious logins, and patching flaws in seconds without waiting for human approval.
- Disconnect Legacy Equipment from the Public Internet. The recent European supermarket attacks succeeded because older industrial controllers were left exposed online. Companies must audit their networks, remove outdated hardware from the open internet, and place operational equipment behind strict firewalls.
- Enforce Zero-Trust Architecture. Instead of trusting any device once it gets inside a company network, Zero-Trust systems require continuous verification for every single action. This stops AI agents from quietly moving from a minor system (like an HVAC controller) to critical servers.
- Adopt Automated Patch Management. Manually testing and rolling out software updates over weeks leaves a massive window for AI attackers. Companies must prioritize rapid, automated patching for internet-facing software and VPNs.
3. Systemic & Policy Measures
At a national and industry level, experts point to three necessary guardrails:
- Secure-by-Design Hardware. Governments and regulators are pushing manufacturers to stop shipping industrial and consumer devices with default passwords or unencrypted connections.
- AI Model Guardrails and Monitoring. AI developers are working to detect and block malicious multi-agent workflows—such as patterns of rapid vulnerability scanning—before attackers can use commercial models to automate breaches.
- Real-Time Threat Sharing. When an AI-driven attack hits one hospital, bank, or utility provider, automated threat-intelligence networks need to share the digital fingerprints of that attack instantly so neighboring organizations can block it automatically.
The Truth Must be Told
Your contribution supports independent journalism
Please take a moment to consider this. Now, more than ever, people are reading Geller Report for news they won't get anywhere else. But advertising revenues have all but disappeared. Google Adsense is the online advertising monopoly and they have banned us. Social media giants like Facebook and Twitter have blocked and shadow-banned our accounts. But we won't put up a paywall. Because never has the free world needed independent journalism more.
Everyone who reads our reporting knows the Geller Report covers the news the media won't. We cannot do our ground-breaking report without your support. We must continue to report on the global jihad and the left's war on freedom. Our readers’ contributions make that possible.
Geller Report's independent, investigative journalism takes a lot of time, money and hard work to produce. But we do it because we believe our work is critical in the fight for freedom and because it is your fight, too.
Please contribute here.
or
Make a monthly commitment to support The Geller Report – choose the option that suits you best.
ADVERTISEMENT
Quick note: We cannot do this without your support. Fact. Our work is made possible by you and only you. We receive no grants, government handouts, or major funding.Tech giants are shutting us down. You know this. Twitter, LinkedIn, Google Adsense, Pinterest permanently banned us. Facebook, Google search et al have shadow-banned, suspended and deleted us from your news feeds. They are disappearing us. But we are here.
Subscribe to Geller Report newsletter here— it’s free and it’s essential NOW when informed decision making and opinion is essential to America's survival. Share our posts on your social channels and with your email contacts. Fight the great fight.
Follow Pamela Geller on Gettr. I am there. click here.
Follow Pamela Geller on Trump's social media platform, Truth Social. It's open and free.
Remember, YOU make the work possible. If you can, please contribute to Geller Report.
Join The Conversation. Leave a Comment.
We have no tolerance for comments containing violence, racism, profanity, vulgarity, doxing, or discourteous behavior. If a comment is spammy or unhelpful, click the ... symbol to the right of the comment to let us know. Thank you for partnering with us to maintain fruitful conversation.



recent Comments